> For those not familiar, there are numerous messages containing images being repeatedly spammed to many Threadiverse users talking about a Polish girl named "Nicole". This has been ongoing for some time now.
>
> Lemmy permits external inline image references to be embedded in messages. This means that if a unique image URL or set of image URLs are sent to each user, it's possible to log the IP addresses that fetch these images; by analyzing the log, one can determine the IP address that a user has.
>
> In some earlier discussion, someone had claimed that local lemmy instances cache these on their local pict-rs instance and rewrite messages to reference the local image.
>
> It does appear that there is a closed issue on the lemmy issue tracker referencing such a deanonymization attack:
>
> https://github.com/LemmyNet/lemmy/issues/1036
>
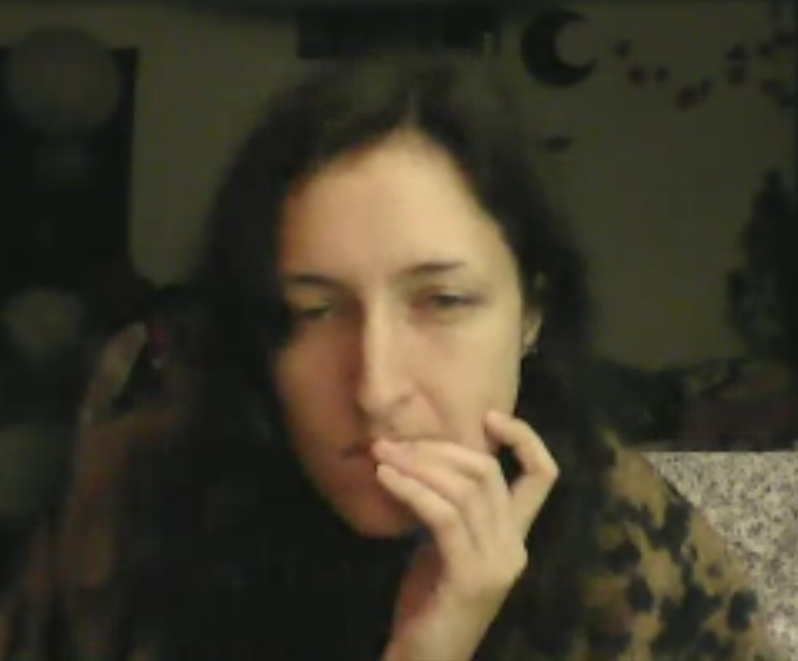
> I had not looked into these earlier, but it looks like such rewriting and caching intending to avoid this attack is not occurring, at least on my home instance. I hadn't looked until the most-recent message, but the image embedded here is indeed remote:
>
>
>
> I haven't stored and looked through a list of these, but as I recall, the user sending them is bouncing around different instances. They certainly are not using the same hostname for their lemmy instance as the pict-rs instance; this message was sent from nicole92 on lemmy.latinlok.com, though the image is hosted on lemmy.doesnotexist.club. I don't know whether they are moving around where the pict-rs instance is located from message to message. If not, it *might* be possible to block the pict-rs instance in your browser. That will only be a temporary fix, since I see no reason that they couldn't also be moving the hostname on the pict-rs instance.
>
> Another mitigation would be to route one's client software or browser through a VPN.
>
> I don't know if there are admins working on addressing the issue; I'd assume so, but I wanted to at least mention that there might be privacy implications to other users.
>
> In any event, regardless of whether the "Nicole" spammer is aiming to deanonymize users, as things stand, it does appear that someone *could* do so.
>
> My own take is that the best fix here on the lemmy-and-other-Threadiverse-software-side would be to disable inline images in messages. Someone who wants to reference an image can always link to an external image in a messages, and permit a user to click through. But if remote inline image references can be used, there's no great way to prevent a user's IP address from being exposed.
>
> If anyone has other suggestions to mitigate this (maybe a Greasemonkey snippet to require a click to load inline images as a patch for the lemmy Web UI?), I'm all ears.