Dark Web Informer :verified_paw: on Nostr: 🚨 Medkey EHR is vulnerable to an IDOR that can expose other patients’ records; ...
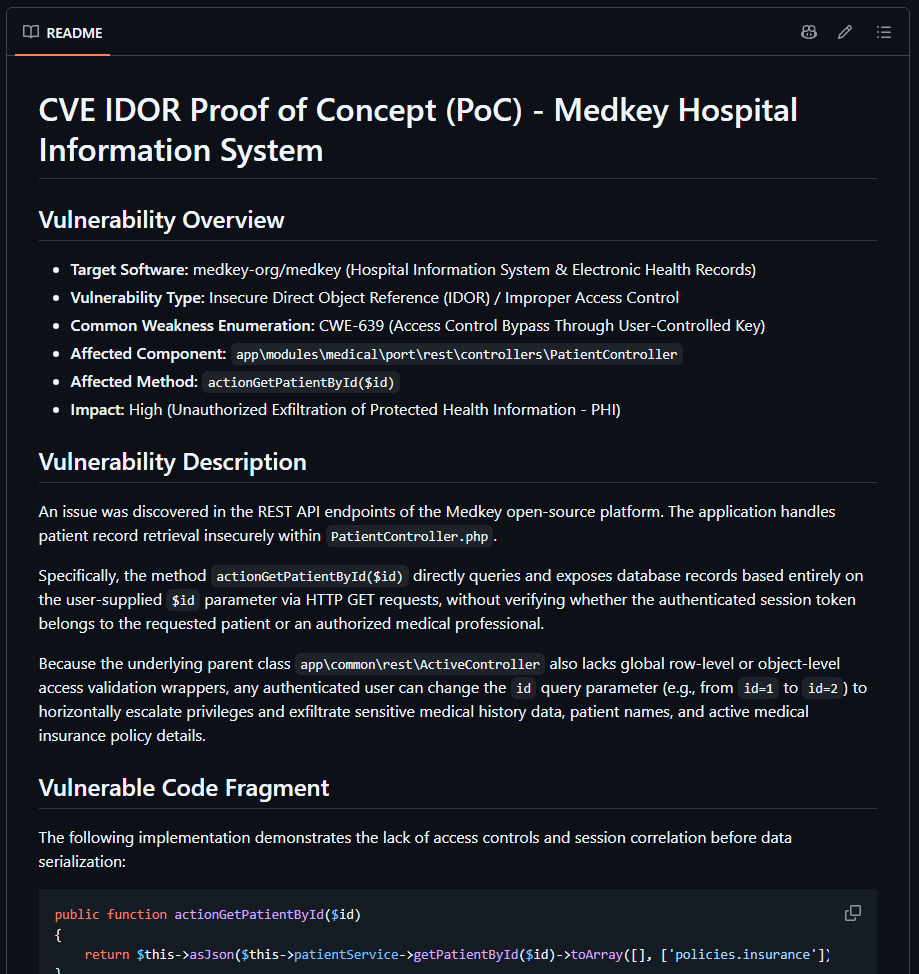
🚨 Medkey EHR is vulnerable to an IDOR that can expose other patients’ records; CVE-2026-12207
PoC:
https://github.com/r0xkrnl/Medkey-EHR-IDOR-PoCThe flaw affects Medkey’s REST API and stems from insufficient authorization checks in the patient lookup functionality. An authenticated user can manipulate a patient ID value and retrieve records belonging to other patients.
CVSS: 4.3 Medium
Impact: Unauthorized access to patient information
Affected: Medkey rolling-release builds through commit fc09b7ba9441ff590b72d428d5380834216b09ed
The issue is tracked as CWE-99, Improper Control of Resource Identifiers, and can be exploited remotely with low privileges and no user interaction.
Published at
2026-10-26 19:14:23 UTCEvent JSON
{
"id": "e11e9b6e1f98ccc0c23fd8a335c0684351527834c670c60957a8bdc262bff1a4",
"pubkey": "3602e3a41b34946d81c007fcf5ae0daae25997b4e04b107e82e56a090c0d9b81",
"created_at": 1793042063,
"kind": 1,
"tags": [
[
"imeta",
"url https://media.infosec.exchange/infosec.exchange/media_attachments/files/117/508/804/614/714/002/original/135e2537055848ae.png",
"m image/png",
"dim 919x974",
"blurhash U14oA-~qRijZ%2tRj]ofIURjt7t7t7Rjflof"
],
[
"proxy",
"https://infosec.exchange/users/DarkWebInformer/statuses/117508804694397087",
"activitypub"
],
[
"client",
"Mostr",
"31990:6be38f8c63df7dbf84db7ec4a6e6fbbd8d19dca3b980efad18585c46f04b26f9:mostr",
"wss://relay.ditto.pub"
]
],
"content": "🚨 Medkey EHR is vulnerable to an IDOR that can expose other patients’ records; CVE-2026-12207\n\nPoC: https://github.com/r0xkrnl/Medkey-EHR-IDOR-PoC\n\nThe flaw affects Medkey’s REST API and stems from insufficient authorization checks in the patient lookup functionality. An authenticated user can manipulate a patient ID value and retrieve records belonging to other patients.\n\nCVSS: 4.3 Medium\nImpact: Unauthorized access to patient information\nAffected: Medkey rolling-release builds through commit fc09b7ba9441ff590b72d428d5380834216b09ed\n\nThe issue is tracked as CWE-99, Improper Control of Resource Identifiers, and can be exploited remotely with low privileges and no user interaction.\n\nhttps://media.infosec.exchange/infosec.exchange/media_attachments/files/117/508/804/614/714/002/original/135e2537055848ae.png",
"sig": "a613515180cb0d50b25802083b60546ad6e4e73b0cf29ecfb76db86dce19564181c67c9564ab11ddd730cf547572b9456020303a6cb9143b4f1acf9e551df62d"
}