Event JSON
{
"id": "c8b1eabff033bbb32390a1930b2940e1bf996d7d929705dc532cb239f6008bee",
"pubkey": "0b1ce4e1dc8078e24b62bd25fbc4d87922afb08441e75a2d90029db566166389",
"created_at": 1765999962,
"kind": 1,
"tags": [
[
"t",
"freebsd"
],
[
"t",
"rtsol"
],
[
"t",
"rtsold"
],
[
"imeta",
"url https://waldvogel.family/system/media_attachments/files/115/736/573/467/012/328/original/0390b0e01bfcde8c.jpg",
"m image/jpeg",
"dim 1671x737",
"blurhash U055FF~qay%M9EWB_3Rj?bt8D%Rj4n_4-;WB"
],
[
"proxy",
"https://waldvogel.family/users/marcel/statuses/115736573554664497",
"activitypub"
],
[
"client",
"Mostr",
"31990:6be38f8c63df7dbf84db7ec4a6e6fbbd8d19dca3b980efad18585c46f04b26f9:mostr",
"wss://relay.ditto.pub/"
]
],
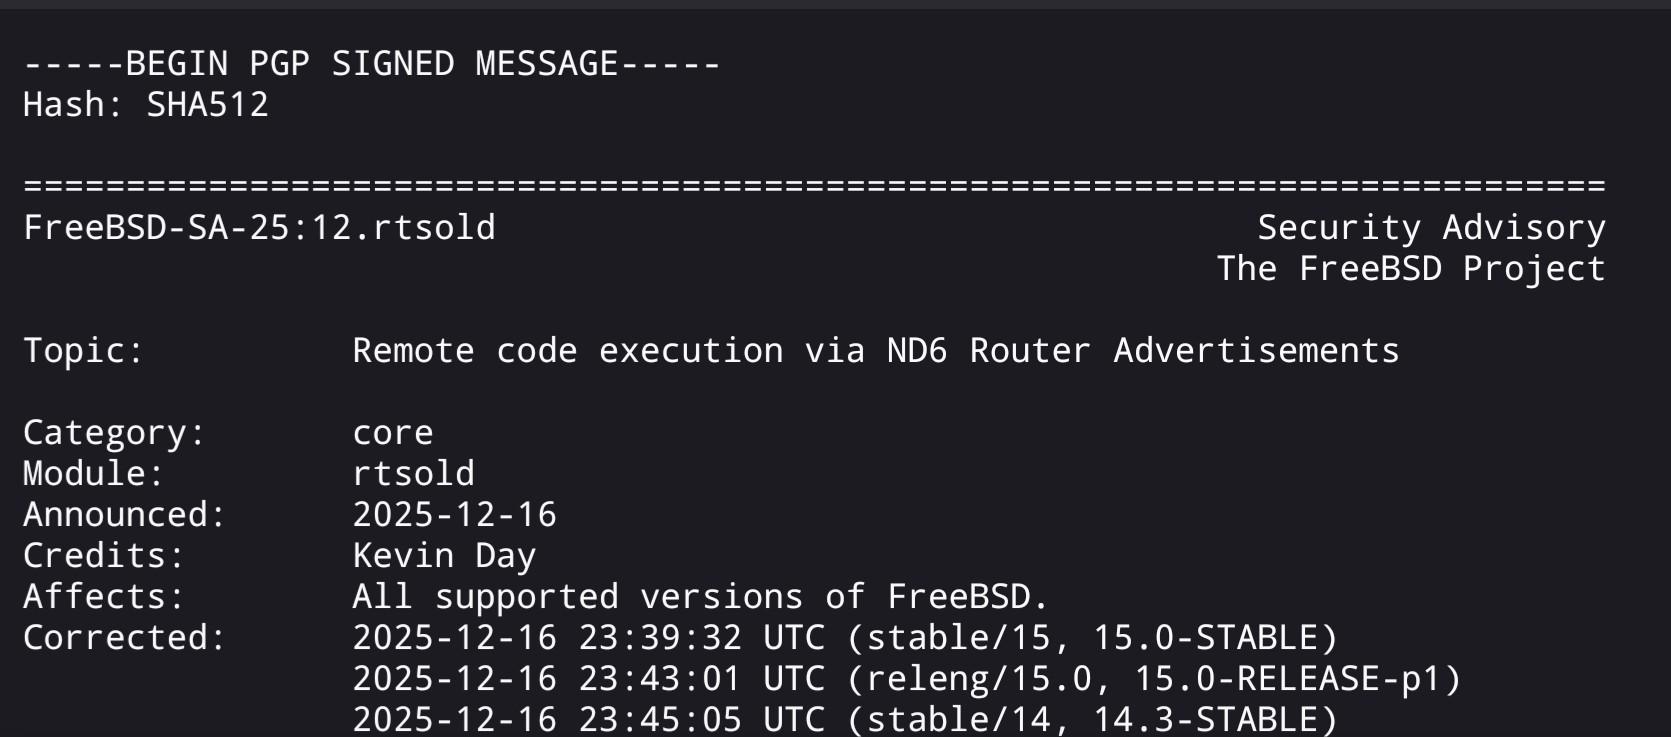
"content": "\"Craft a single network packet to obtain root\": I had hoped that this type of vulnerability hat been eliminated.\n\nAt least, the Router Advertisement packets should generally not be able to cross routers.\n\nPatch your #FreeBSD systems now.\n#rtsol #rtsold\nhttps://www.freebsd.org/security/advisories/FreeBSD-SA-25:12.rtsold.asc\n\nhttps://waldvogel.family/system/media_attachments/files/115/736/573/467/012/328/original/0390b0e01bfcde8c.jpg",
"sig": "190e224b90e67684a19186723851eede76489a21b98264bf3248f227bf577eef8343155a32ba5fb58ae1a40454d246910bf1b56975fd83446b8f940ae93029d3"
}