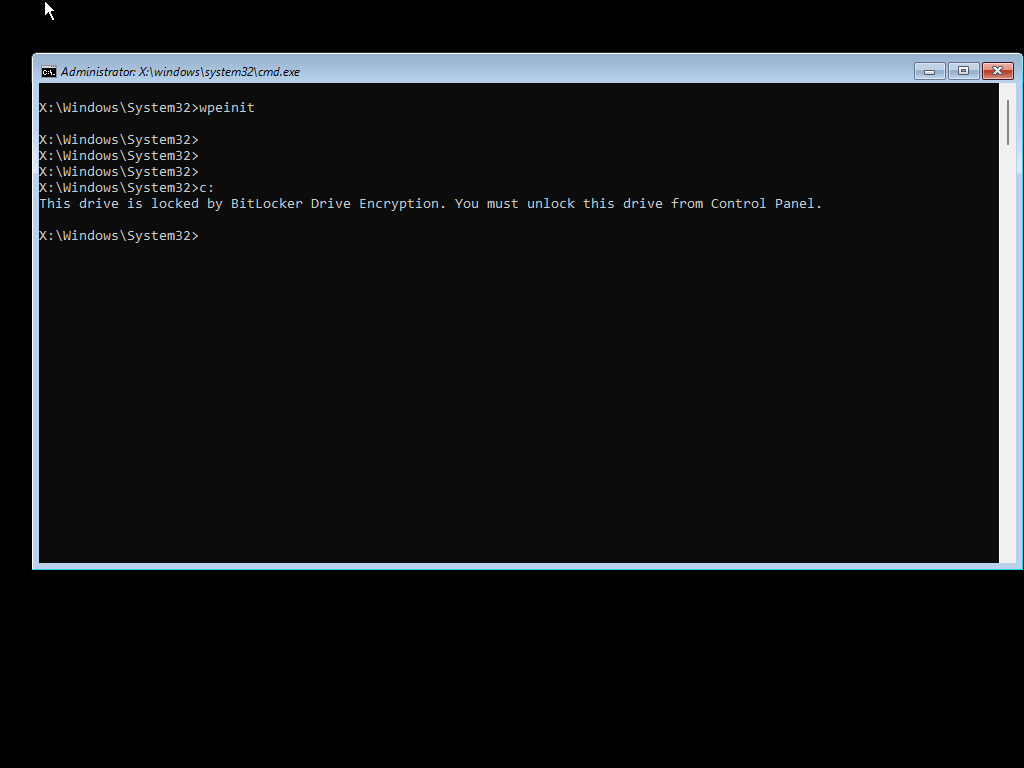
Specifically, you prevent the FsTx Auto Recovery Utility, autofstx.exe, from automatically starting when the WinRE image launches.
With this change, the Transactional NTFS replaying that deletes winpeshl.ini no longer happens. It also recommends switching from TPM-only to TPM+PIN.
**But wait!**, you clever security-conscious person exclaims. If the WinRE partition is unencrypted, what stops an attacker from simply splatting back a **vulnerable** WinRE partition/image? You are right, you can indeed do this and you'll get a CMD prompt when WinRE is entered. **However**, the modification of WinRE will cause the trust relationship between bitlocker and WinRE to fail. And as such, while you are at your handy cmd.exe prompt, you will **not** get an automatically-decrypted bitlocker partition.