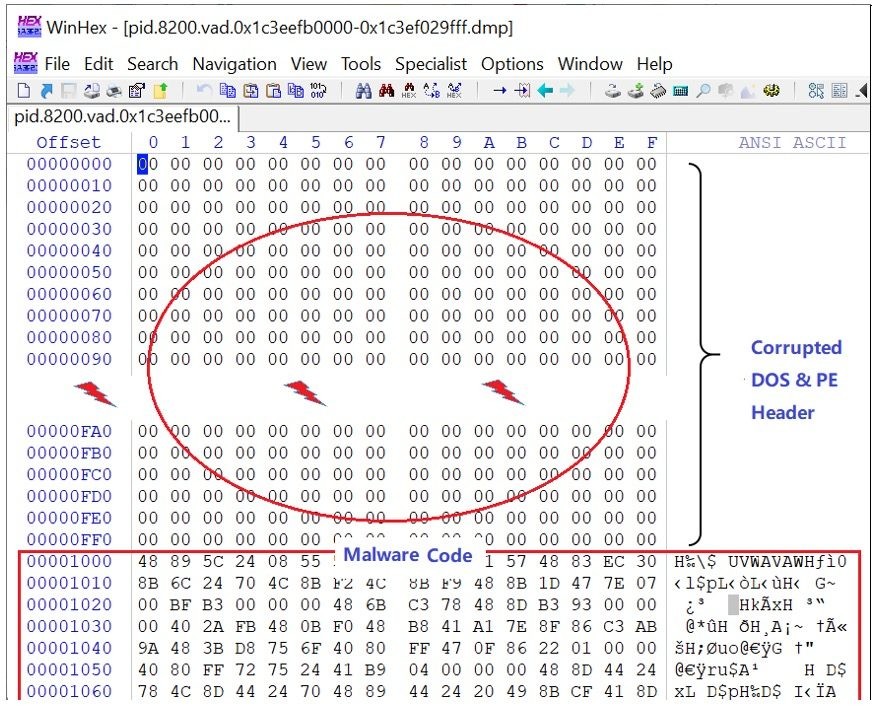
FortiGuard Labs (npub1a90…kugv) dropped a deep dive into a malware sample dumped without a PE header — like a cybercriminal rage-quit halfway through packing their payload.
You ever load a binary in IDA and think, “Am I being punk’d?”
Yeah, it’s one of those samples.
This sample:<li><p>Reconstructs its own PE structure at runtime</p></li><li><p>Hides config data in obfuscated blobs</p></li><li><p>Uses anti-sandbox tricks to avoid analysis</p></li><li><p>Drops yet another info-stealer, because originality is dead</p></li>
It’s engineered to break basic static analysis and dodge sandboxes like it’s speedrunning DEFCON CTF.
🔗 Full breakdown:
https://www.fortinet.com/blog/threat-research/deep-dive-into-a-dumped-malware-without-a-pe-header
TL;DR for blue teamers:<li><p>Static AV signatures won’t help here</p></li><li><p>Watch for suspicious memory allocations + hollowing patterns</p></li><li><p>Endpoint heuristics > file-based detection</p></li><li><p>Log your PowerShell and LOLBins — this thing probably brings friends</p></li><li><p>If your EDR cries when it sees raw shellcode, maybe give it a hug</p></li>
#ThreatIntel #MalwareAnalysis #ReverseEngineering #Infosec #PEFilesAreSo2020 #EDREvasion #LOLbins #CyberSecurity #BlueTeam