:rainbowCrow: on Nostr: Palo finally published an advisory outlining impact from CVE-2026-111497 in brotli. A ...
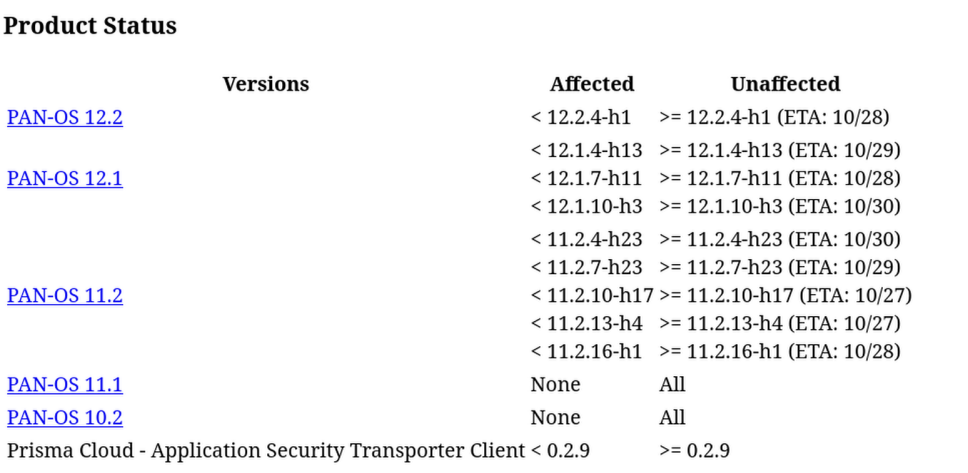
Palo finally published an advisory outlining impact from CVE-2026-111497 in brotli.
https://security.paloaltonetworks.com/CVE-2026-111497A buffer overflow vulnerability in the Brotli decoder (c/dec/decode.c) in Google Brotli versions 1.0.3 through 1.2.0 on all platforms allows a remote unauthenticated attacker to corrupt adjacent decoder state memory, disclose sensitive memory contents, cause a denial of service, or potentially execute arbitrary code using a crafted Brotli-compressed stream. Users need to update any Brotli libraries or binaries between 1.0.3 through 1.2.0 to the latest available version: 1.0.10 or 1.1.1 or 1.2.1. Brotli is commonly used by many HTTP-based applications including Node.js.
Most importantly:
This issue is applicable to PAN-OS software on PA-Series and VM-Series firewalls that have inspection of Brotli compressed traffic and TLS/SSL decryption enabled on the dataplane. There is no impact on the Management interface (web or API) of the PAN-OS devices.
Published at
2026-10-26 19:13:58 UTCEvent JSON
{
"id": "8148f24f4c2419e1ab73128f0d71638927e079fd5d8de4cbe0074bc8bfada2de",
"pubkey": "14609e2d429cc6b47de05d41a9840716e4d2e0bec59e8bbf79ad79dd7c5def64",
"created_at": 1793042038,
"kind": 1,
"tags": [
[
"imeta",
"url https://media.infosec.exchange/infosec.exchange/media_attachments/files/117/508/798/536/612/082/original/e9949286208aa0b4.png",
"m image/png",
"dim 968x473",
"blurhash UBS6Pn?dIY4p_2t6RifO%L4nj?xu_3t5Rjax"
],
[
"proxy",
"https://infosec.exchange/users/cR0w/statuses/117508803052807673",
"activitypub"
],
[
"client",
"Mostr",
"31990:6be38f8c63df7dbf84db7ec4a6e6fbbd8d19dca3b980efad18585c46f04b26f9:mostr",
"wss://relay.ditto.pub"
]
],
"content": "Palo finally published an advisory outlining impact from CVE-2026-111497 in brotli.\n\nhttps://security.paloaltonetworks.com/CVE-2026-111497\n\nA buffer overflow vulnerability in the Brotli decoder (c/dec/decode.c) in Google Brotli versions 1.0.3 through 1.2.0 on all platforms allows a remote unauthenticated attacker to corrupt adjacent decoder state memory, disclose sensitive memory contents, cause a denial of service, or potentially execute arbitrary code using a crafted Brotli-compressed stream. Users need to update any Brotli libraries or binaries between 1.0.3 through 1.2.0 to the latest available version: 1.0.10 or 1.1.1 or 1.2.1. Brotli is commonly used by many HTTP-based applications including Node.js.\n\nMost importantly:\n\nThis issue is applicable to PAN-OS software on PA-Series and VM-Series firewalls that have inspection of Brotli compressed traffic and TLS/SSL decryption enabled on the dataplane. There is no impact on the Management interface (web or API) of the PAN-OS devices.\n\nhttps://media.infosec.exchange/infosec.exchange/media_attachments/files/117/508/798/536/612/082/original/e9949286208aa0b4.png",
"sig": "9c2d801fd1b831abb9cb1938b10b0e0d8b729a274704dcc6e3190bb42c18a68b2d73177bf52547528a28e4a7378ea3cdc768472a0fbae3eb4bbb760e7948d410"
}