Dark Web Informer :verified_paw: on Nostr: 🚨 Microsoft 365 token replay campaign compromises 97 accounts across 79 ...
🚨 Microsoft 365 token replay campaign compromises 97 accounts across 79 organizations
Huntress tracked more than 200,000 login attempts and 497 successful sign-ins during the campaign, which ran from July 14 to September 22.
⠀
Attackers used adversary-in-the-middle phishing pages to steal authenticated Microsoft sessions, allowing them to bypass MFA by replaying the captured tokens from their own systems.
After gaining access, the attackers registered at least 48 rogue Entra devices, replaced victims’ MFA methods and created hidden inbox rules to conceal messages involving payroll, direct deposits, banking and bonuses.
⠀
In 19 organizations, existing MFA methods were removed and replaced within three hours of the initial compromise.
Organizations should revoke affected sessions, reset passwords, audit Entra devices and MFA methods, review inbox rules and restrict device-code authentication through Conditional Access.
Source:
https://www.huntress.com/blog/token-replay-spray 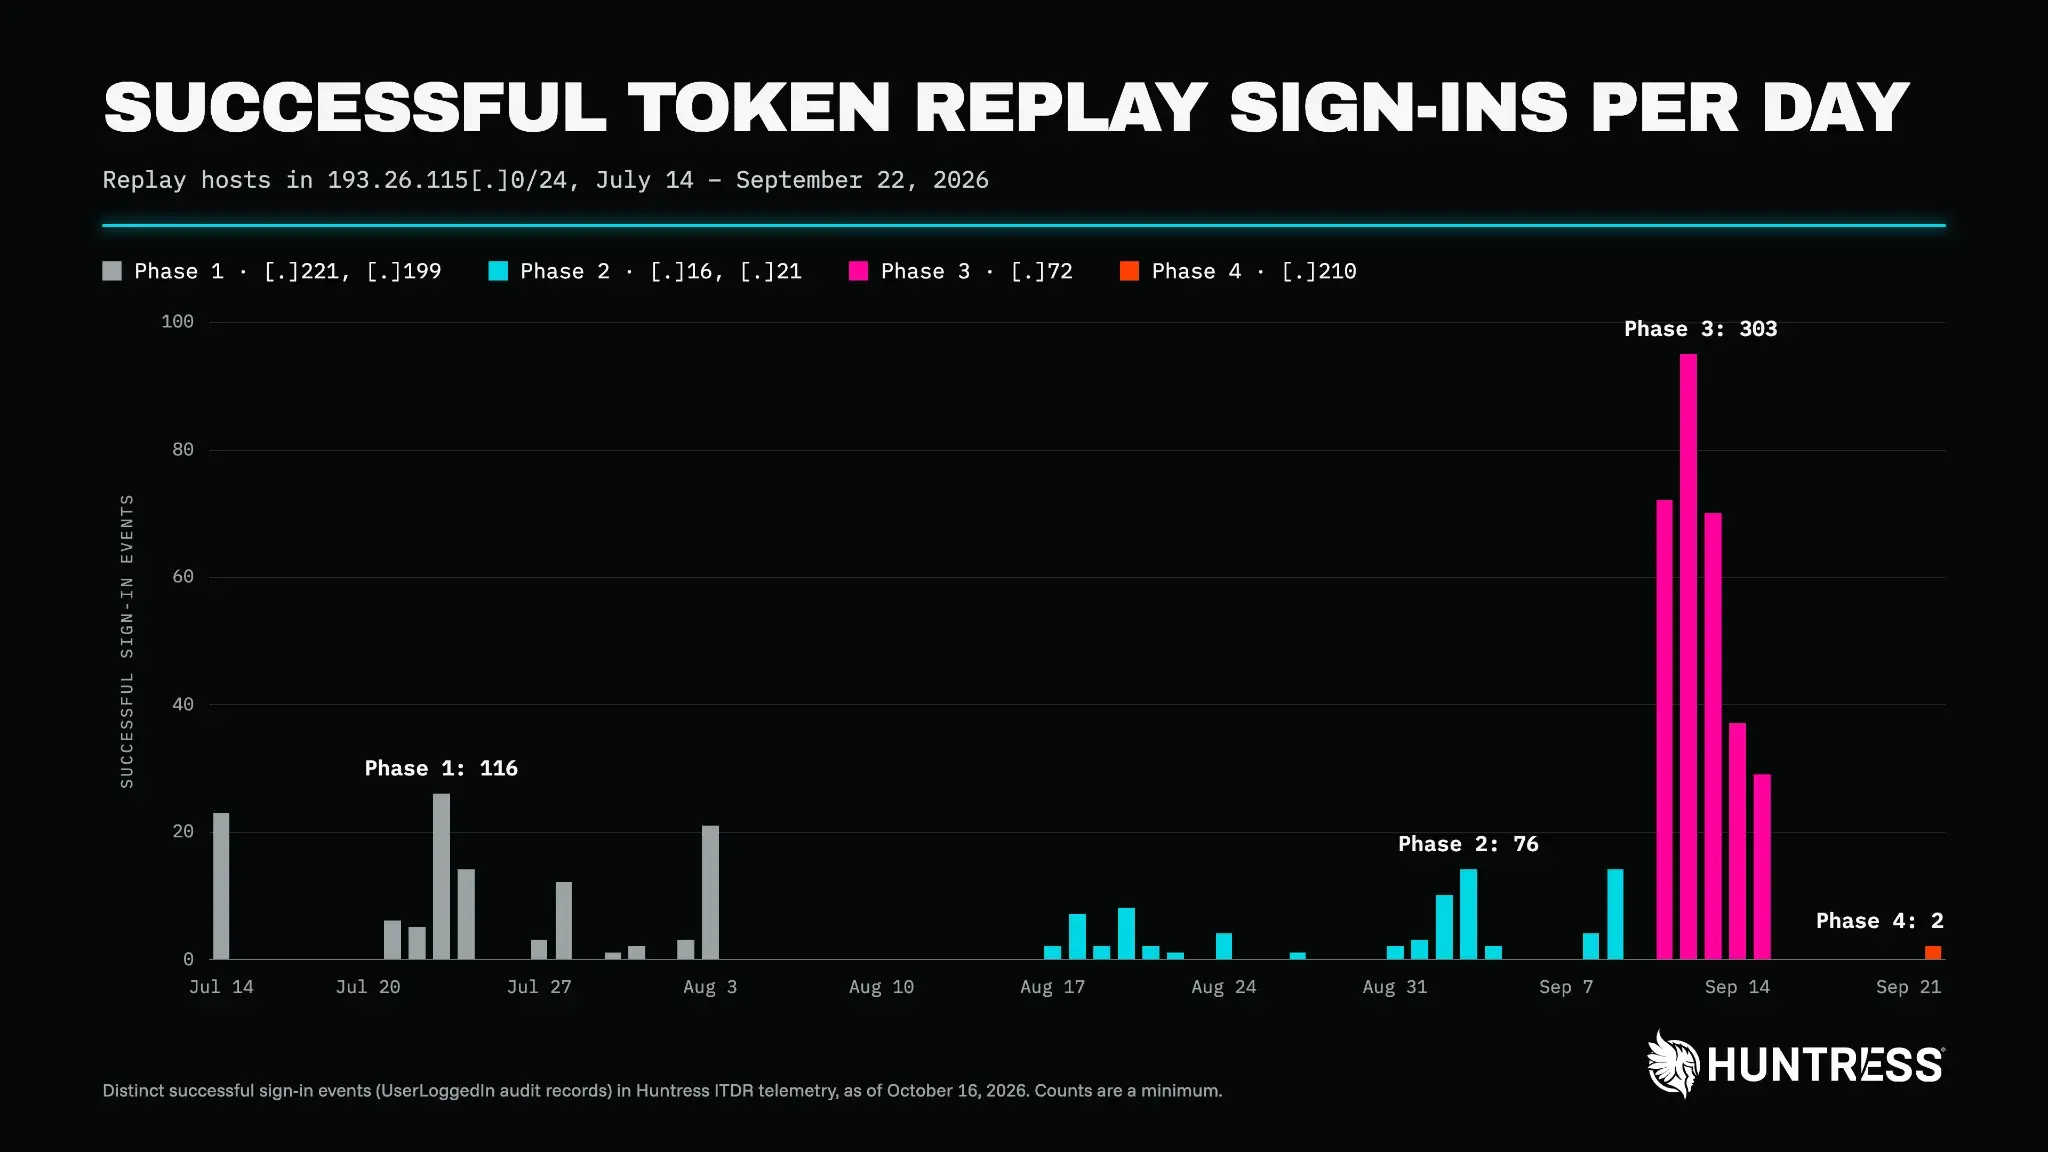
Published at
2026-10-26 14:34:25 UTCEvent JSON
{
"id": "83b9416cc9935c7c7e55b0c57ee1742999d257d6d0d82c21eb4ce334298fcc19",
"pubkey": "3602e3a41b34946d81c007fcf5ae0daae25997b4e04b107e82e56a090c0d9b81",
"created_at": 1793025265,
"kind": 1,
"tags": [
[
"imeta",
"url https://media.infosec.exchange/infosec.exchange/media_attachments/files/117/507/703/770/509/514/original/aa480641730c74fc.webp",
"m image/webp",
"dim 2048x1152",
"blurhash U34_e7B4w3of?u$+I.s:?]wNNGbH~WS_nPof"
],
[
"proxy",
"https://infosec.exchange/users/DarkWebInformer/statuses/117507703830811673",
"activitypub"
],
[
"client",
"Mostr",
"31990:6be38f8c63df7dbf84db7ec4a6e6fbbd8d19dca3b980efad18585c46f04b26f9:mostr",
"wss://relay.ditto.pub"
]
],
"content": "🚨 Microsoft 365 token replay campaign compromises 97 accounts across 79 organizations\n\nHuntress tracked more than 200,000 login attempts and 497 successful sign-ins during the campaign, which ran from July 14 to September 22.\n⠀\nAttackers used adversary-in-the-middle phishing pages to steal authenticated Microsoft sessions, allowing them to bypass MFA by replaying the captured tokens from their own systems.\n\nAfter gaining access, the attackers registered at least 48 rogue Entra devices, replaced victims’ MFA methods and created hidden inbox rules to conceal messages involving payroll, direct deposits, banking and bonuses.\n⠀\nIn 19 organizations, existing MFA methods were removed and replaced within three hours of the initial compromise.\n\nOrganizations should revoke affected sessions, reset passwords, audit Entra devices and MFA methods, review inbox rules and restrict device-code authentication through Conditional Access.\n\nSource: https://www.huntress.com/blog/token-replay-spray\n\nhttps://media.infosec.exchange/infosec.exchange/media_attachments/files/117/507/703/770/509/514/original/aa480641730c74fc.webp",
"sig": "f0838d7c9d29afa86c443037e57d1afb974c6c25216993d5150becfedbc3070fd8bf22a1b9e546c2b46f1f0d30327b437110d589e01fb8b1ad1a4066b78d1074"
}