Event JSON
{
"id": "5728a34a17a66be4f61cac2ca0bc8dd6f115e4ea11e8a1ce21e63294d84c027b",
"pubkey": "5e4fde2d08a17a34bf773c36b8d53c0c7c778e9985af96ae3a7ce404ba376940",
"created_at": 1762000747,
"kind": 1,
"tags": [
[
"imeta",
"url https://media.infosec.exchange/infosec.exchange/media_attachments/files/115/474/477/612/174/308/original/ee8cbaf2c8da7b9e.png",
"m image/png"
],
[
"proxy",
"https://infosec.exchange/@harrysintonen/115474480965441636",
"web"
],
[
"t",
"vulnerability"
],
[
"t",
"mantisbt"
],
[
"t",
"cybersecurity"
],
[
"t",
"infosec"
],
[
"t",
"cve_2025_47776"
],
[
"proxy",
"https://infosec.exchange/users/harrysintonen/statuses/115474480965441636",
"activitypub"
],
[
"L",
"pink.momostr"
],
[
"l",
"pink.momostr.activitypub:https://infosec.exchange/users/harrysintonen/statuses/115474480965441636",
"pink.momostr"
],
[
"-"
]
],
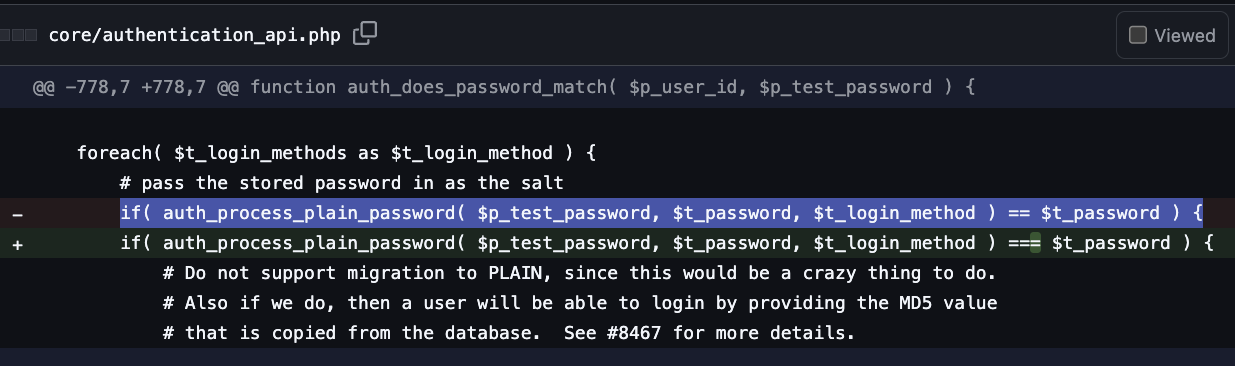
"content": "Several months ago, I found a #vulnerability from #MantisBT - Authentication bypass for some passwords due to PHP type juggling (CVE-2025-47776).\n\nAny account that has a password that results in a hash that matches ^0+[Ee][0-9]+$ can be logged in with a password that matches that regex as well. For example, password comito5 can be used to log in to the affected accounts and thus gain unauthorised access.\n\nThe root cause of this bug is the incorrect use of == to match the password hash:\n\nif( auth_process_plain_password( $p_test_password, $t_password, $t_login_method ) == $t_password )\n\nThe fix is to use === for the comparison.\n\nThis vulnerability has existed in MantisBT ever since hashed password support was added (read: decades). MantisBT 2.27.2 and later include a fix to this vulnerability. https://mantisbt.org/download.php\n\n#CVE_2025_47776 #infosec #cybersecurity\nhttps://media.infosec.exchange/infosec.exchange/media_attachments/files/115/474/477/612/174/308/original/ee8cbaf2c8da7b9e.png\n",
"sig": "115f377505fcc0795b7efb00bfed490dd0512c3b6566688c64c6de2fedce52cc66906e598cbdeeaedc17d5512aca2107ee8d2658f2bb22b91b2c62f4399f33a5"
}