Event JSON
{
"id": "509dd89d0ef5487f85cb3813257049fdfb9db5b63d6c85190f760b307457a23f",
"pubkey": "5f36df27154ca6a4612c0cddecb1ee363a23ff9c00e265e36626740f2e6224a4",
"created_at": 1780492828,
"kind": 1,
"tags": [
[
"t",
"cybersecurity"
],
[
"t",
"supplychainsecurity"
],
[
"t",
"npm"
],
[
"t",
"redhat"
],
[
"imeta",
"url https://cdn.masto.host/mastodonuno/media_attachments/files/116/686/370/679/110/603/original/343346a7617a647a.png",
"m image/png",
"dim 1254x1254",
"blurhash U88DLr-;s:wJ}txaniwJ=|-pj[r?V@w{WBn%"
],
[
"proxy",
"https://mastodon.uno/users/nextredblog/statuses/116686377996434895",
"activitypub"
],
[
"client",
"Mostr",
"31990:6be38f8c63df7dbf84db7ec4a6e6fbbd8d19dca3b980efad18585c46f04b26f9:mostr",
"wss://relay.ditto.pub"
]
],
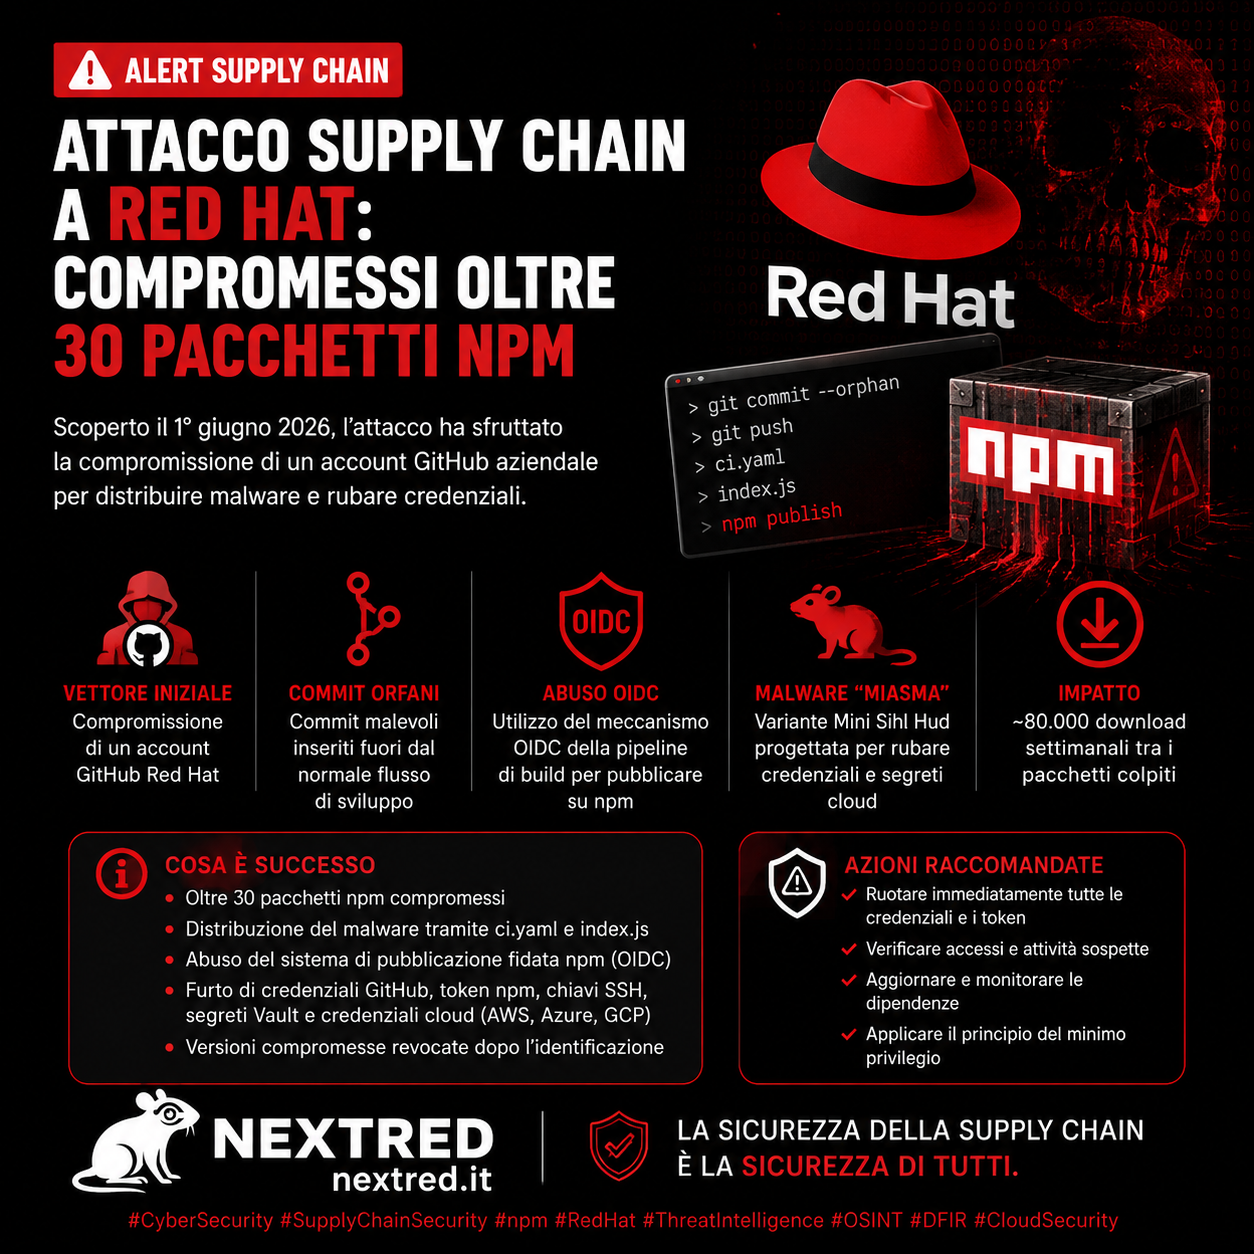
"content": "🚨 Supply chain attack contro Red Hat: compromessi oltre 30 pacchetti npm dopo la violazione di un account GitHub aziendale.\n\nIl malware \"Miasma\" puntava a rubare token, chiavi SSH e credenziali cloud (AWS, Azure, GCP). I pacchetti colpiti registravano circa 80.000 download settimanali.\n\n⚠️Versioni malevole revocate, raccomandata la rotazione immediata delle credenziali.\n\n#CyberSecurity #SupplyChainSecurity #npm #RedHat\n\nhttps://cdn.masto.host/mastodonuno/media_attachments/files/116/686/370/679/110/603/original/343346a7617a647a.png",
"sig": "3a301e0185916eb4535787ec6f5f6f14880bba0de16d3c9b9f92a8c9dfc202cc5c01b697fed611ce14f8c6ace976ff596fab3c127f486285f6fd38b895db18cb"
}