Event JSON
{
"id": "77890cd169f2297e3582aedcf790525b5928449263f10d68fbba39f08d75b3af",
"pubkey": "c66d7f1e186bed50c2846d3c55becbfda7593229815db5d55e4079d4d12ad39d",
"created_at": 1792659684,
"kind": 1,
"tags": [
[
"t",
"mythicratatoskr"
],
[
"t",
"esetresearch"
],
[
"imeta",
"url https://media.infosec.exchange/infosec.exchange/media_attachments/files/117/483/745/015/386/186/original/f1d261d11c53ab62.png",
"m image/png"
],
[
"proxy",
"https://infosec.exchange/@ESETresearch/117483745098199962",
"web"
],
[
"t",
"matchwok"
],
[
"t",
"sandworm"
],
[
"t",
"yggdrasil"
],
[
"t",
"uac"
],
[
"proxy",
"https://infosec.exchange/users/ESETresearch/statuses/117483745098199962",
"activitypub"
],
[
"L",
"pink.momostr"
],
[
"l",
"pink.momostr.activitypub:https://infosec.exchange/users/ESETresearch/statuses/117483745098199962",
"pink.momostr"
],
[
"-"
]
],
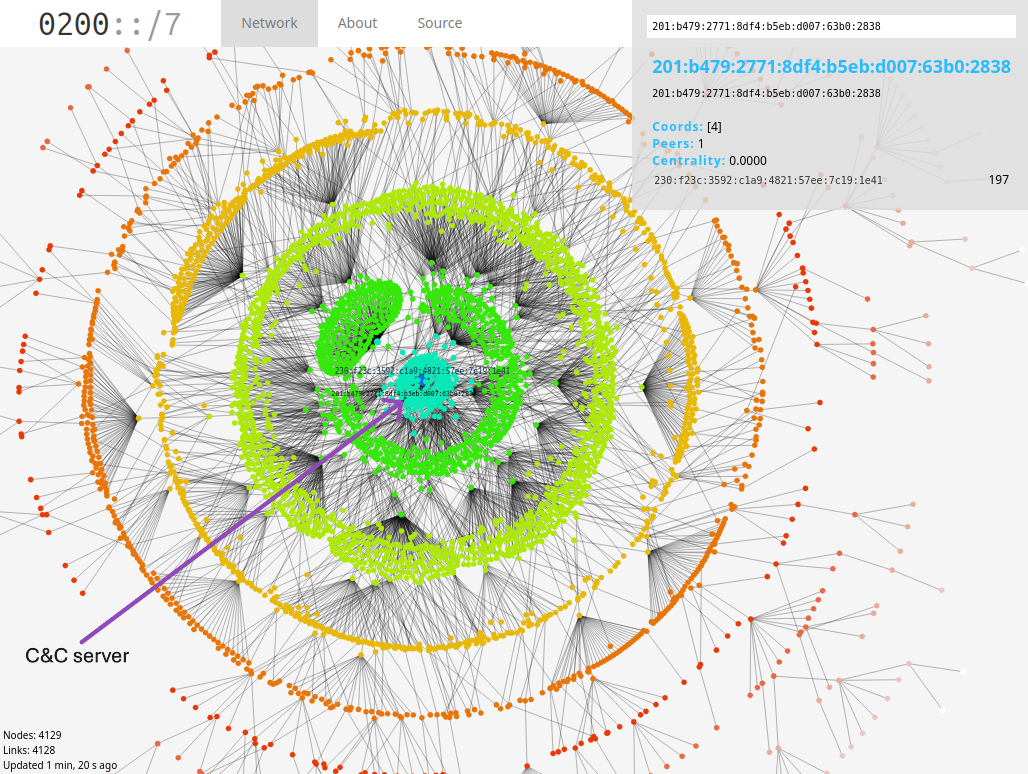
"content": "#ESETresearch uncovered #MythicRatatoskr, an undocumented Go backdoor hiding its C\u0026C server inside the #Yggdrasil mesh network. It was used against a Ukrainian 🇺🇦 grain logistics firm in an intrusion that ended in a destructive #Sandworm attack.\nhttps://www.welivesecurity.com/en/eset-research/mythicratatoskr-yggdrasil-enabled-backdoor-deployed-uac0099-sandworm-collaboration/ \nOn July 16th, 2025, #UAC 0099 gained initial access via a spearphishing email, leading to an execution chain dropping the #MATCHWOK backdoor. One day later, the attackers deployed a previously unknown backdoor we named MythicRatatoskr.\n#Yggdrasil is a decentralized, end-to-end-encrypted IPv6 mesh network. Nodes are addressed by their public keys, and no central server runs the mesh – making it hard to disrupt. To our knowledge, this is the first documented abuse of Yggdrasil by a state-aligned threat actor.\nYggdrasil is not designed for anonymity, so we generated a map of the network’s spanning tree to locate the C\u0026C server. It sits near the center of the tree, making it easily reachable from other peers.\nTwo months later, on September 17th, 2025, #Sandworm wiped data across the company’s network using SDelete deployed via Active Directory Group Policy. We assess with high confidence that UAC 0099 handed off access to Sandworm during the intrusion.\nIoCs are available in our GitHub repo: https://github.com/eset/malware-ioc/tree/master/mythicratatoskr\nhttps://media.infosec.exchange/infosec.exchange/media_attachments/files/117/483/745/015/386/186/original/f1d261d11c53ab62.png\n",
"sig": "f2d9de2af6fe1627644201ded8482f59876bb6843b345031fa111bb1a990e4c672f15988ef2fc8837d60a4950e423ed6c55ffc7c434738764ad4f3db69837f1f"
}