Paco Hope on Nostr: This one boggles my mind. I use DNSMadeEasy as my public DNS for my high-traffic ...
This one boggles my mind. I use DNSMadeEasy as my public DNS for my high-traffic domains. I give them my records, they publish them. No biggie.
My monthly quota is 10M queries. On a web site that has 30 MAU, the DNS requests should be WAY under that number.
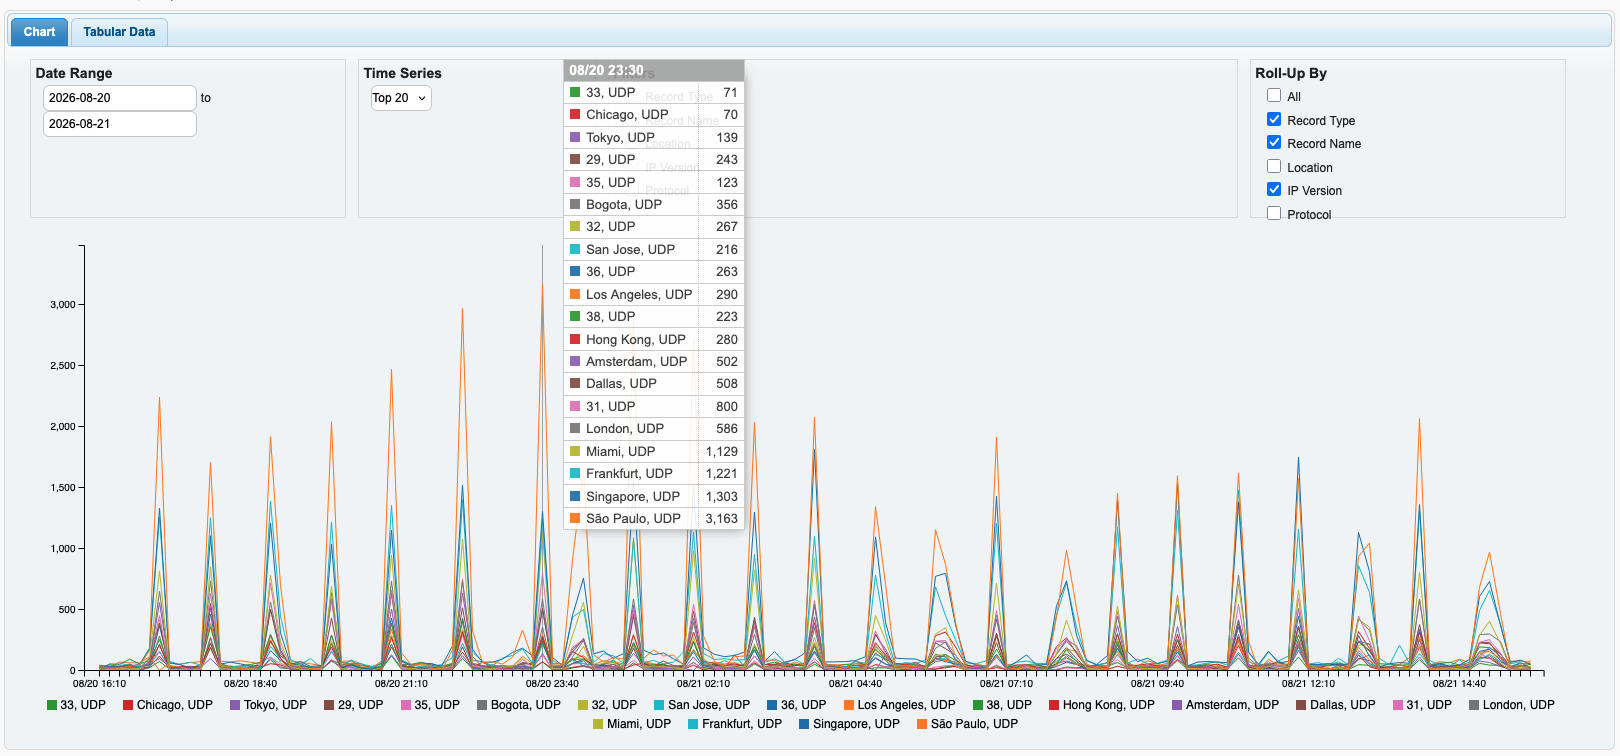
But I'm seeing these super regular spikes and they're high. I'm 21 days into the month and I'm 9.6M queries so far. If I exceed 10M queries, I'll end up paying $6 for another 1M queries. But I don't know how to stop the queries. Unlike a CDN, where I could receive the HTTPS request and say "no page for you," I can't stop UDP DNS requests (can I?)
So if these are real DNS requests (e.g., from scraping bots) what can I do? I do not have a lot of Latin American or South American traffic. These spikes can't be related to real usage.
Published at
2026-08-21 18:27:20 UTCEvent JSON
{
"id": "ffded3c31b1189ae2381498ad78e58a60d658bec98f2170281bd17f996c12b8c",
"pubkey": "3edacd527e301af6df8f3968b768d6b1b77c8f3682010d3de7f4d07a531bc82c",
"created_at": 1787336840,
"kind": 1,
"tags": [
[
"imeta",
"url https://media.infosec.exchange/infosec.exchange/media_attachments/files/117/134/890/588/541/548/original/7778d62c225ca070.png",
"m image/png"
],
[
"proxy",
"https://infosec.exchange/@paco/117134907182557158",
"web"
],
[
"proxy",
"https://infosec.exchange/users/paco/statuses/117134907182557158",
"activitypub"
],
[
"L",
"pink.momostr"
],
[
"l",
"pink.momostr.activitypub:https://infosec.exchange/users/paco/statuses/117134907182557158",
"pink.momostr"
],
[
"-"
]
],
"content": "This one boggles my mind. I use DNSMadeEasy as my public DNS for my high-traffic domains. I give them my records, they publish them. No biggie. \n\nMy monthly quota is 10M queries. On a web site that has 30 MAU, the DNS requests should be WAY under that number.\n\nBut I'm seeing these super regular spikes and they're high. I'm 21 days into the month and I'm 9.6M queries so far. If I exceed 10M queries, I'll end up paying $6 for another 1M queries. But I don't know how to stop the queries. Unlike a CDN, where I could receive the HTTPS request and say \"no page for you,\" I can't stop UDP DNS requests (can I?)\n\nSo if these are real DNS requests (e.g., from scraping bots) what can I do? I do not have a lot of Latin American or South American traffic. These spikes can't be related to real usage.\nhttps://media.infosec.exchange/infosec.exchange/media_attachments/files/117/134/890/588/541/548/original/7778d62c225ca070.png\n",
"sig": "eb37d0aaf884dbfddc8e8530c667b2581cda8fc1f5e942c24e74e89839c9f9f9bbdfd1982b9200379dc5ec02b32f721b3232aed0ec63e5b577068a76519b5635"
}
