Dark Web Informer :verified_paw: on Nostr: 🚨🇧🇷 Vakinha Dataset Allegedly Leaked After Ransom Demand A dataset allegedly ...
🚨🇧🇷 Vakinha Dataset Allegedly Leaked After Ransom Demand
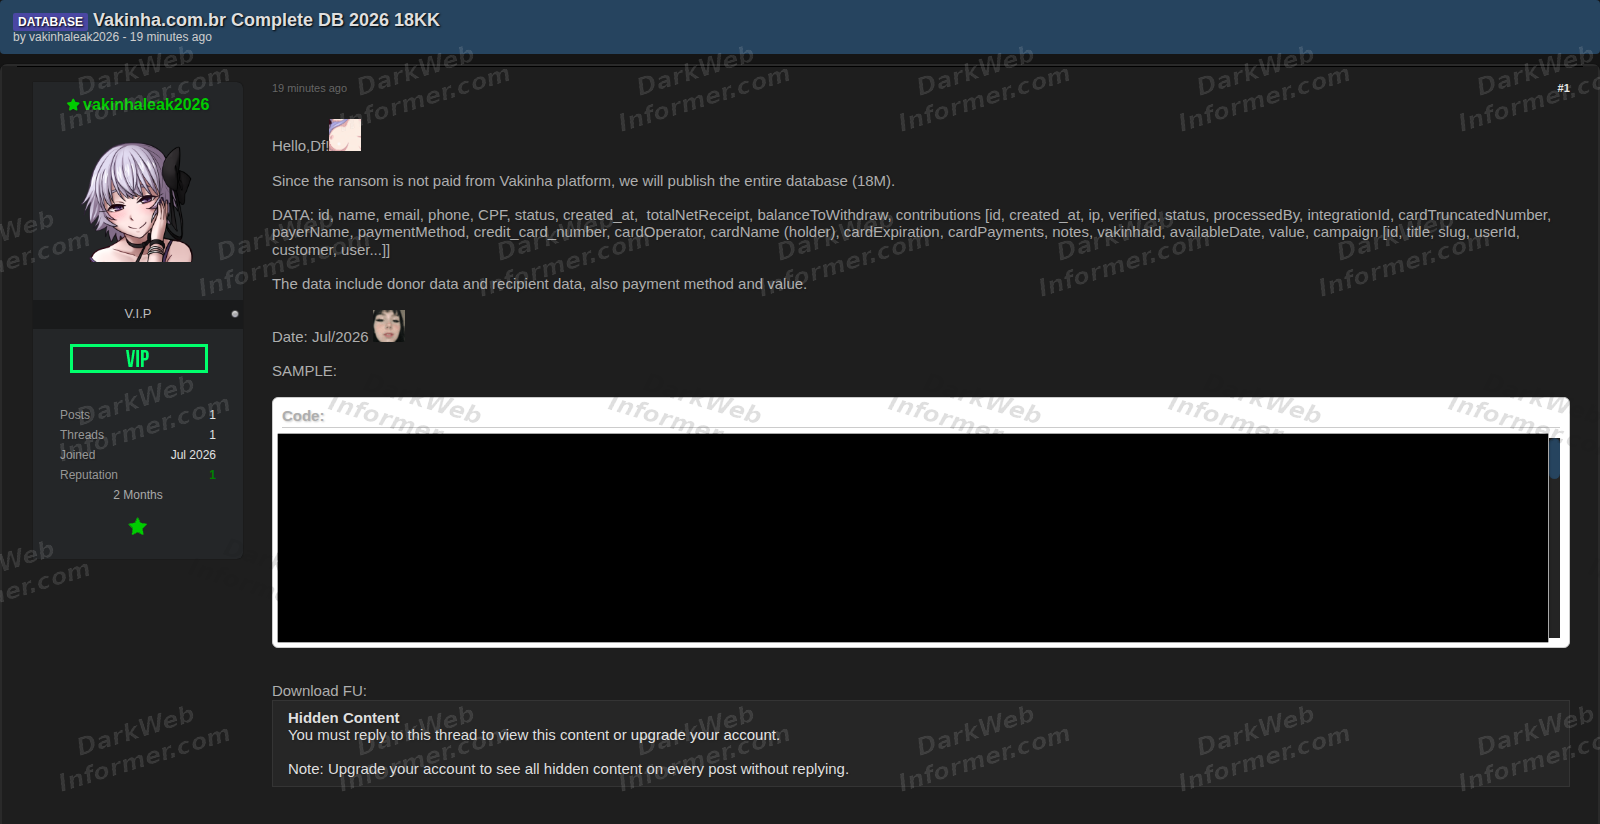
A dataset allegedly belonging to Brazilian crowdfunding platform Vakinha has been shared on a forum after the actor claimed a ransom was not paid.
The post claims the dataset contains approximately 18 million records and includes donor and recipient information.
According to the actor, exposed fields include names, email addresses, phone numbers, CPF numbers, IP addresses, payment methods, transaction values, campaign information, and other account-related data.
A sample of the purported data was included in the post, which lists the material as dating from July 2026.
These claims have not been independently verified.
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing
Published at
2026-09-28 23:27:45 UTCEvent JSON
{
"id": "fbc33867a074fcf4ea6dd82a1cb5975fb347bb8f9ea3c6b849ca47e2847751ac",
"pubkey": "74529fa3c8adf20d73e8e245536c5663db200537f90661d797c4fcab839459d7",
"created_at": 1790638065,
"kind": 1,
"tags": [
[
"imeta",
"url https://media.infosec.exchange/infosec.exchange/media_attachments/files/117/351/256/193/100/523/original/82a255c4149ad3bf.png",
"m image/png"
],
[
"proxy",
"https://infosec.exchange/@DarkWebInformer/117351256247747225",
"web"
],
[
"proxy",
"https://infosec.exchange/users/DarkWebInformer/statuses/117351256247747225",
"activitypub"
],
[
"L",
"pink.momostr"
],
[
"l",
"pink.momostr.activitypub:https://infosec.exchange/users/DarkWebInformer/statuses/117351256247747225",
"pink.momostr"
],
[
"-"
]
],
"content": "🚨🇧🇷 Vakinha Dataset Allegedly Leaked After Ransom Demand\n\nA dataset allegedly belonging to Brazilian crowdfunding platform Vakinha has been shared on a forum after the actor claimed a ransom was not paid.\n\nThe post claims the dataset contains approximately 18 million records and includes donor and recipient information.\n\nAccording to the actor, exposed fields include names, email addresses, phone numbers, CPF numbers, IP addresses, payment methods, transaction values, campaign information, and other account-related data.\n\nA sample of the purported data was included in the post, which lists the material as dating from July 2026.\n\nThese claims have not been independently verified.\n\n💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. darkwebinformer.com/pricing\nhttps://media.infosec.exchange/infosec.exchange/media_attachments/files/117/351/256/193/100/523/original/82a255c4149ad3bf.png\n",
"sig": "90c5ada3499427105f3664af7c1e78ea8faf495e599283663c040103d99ee2ba17a176b5cf3edddaf04aec9045b0dbcd61e0683f76d40c00dd5b4d4fc000f55a"
}